Requirements change, but Operational Excellence should stay the same
The universal framework for management of any Third Party
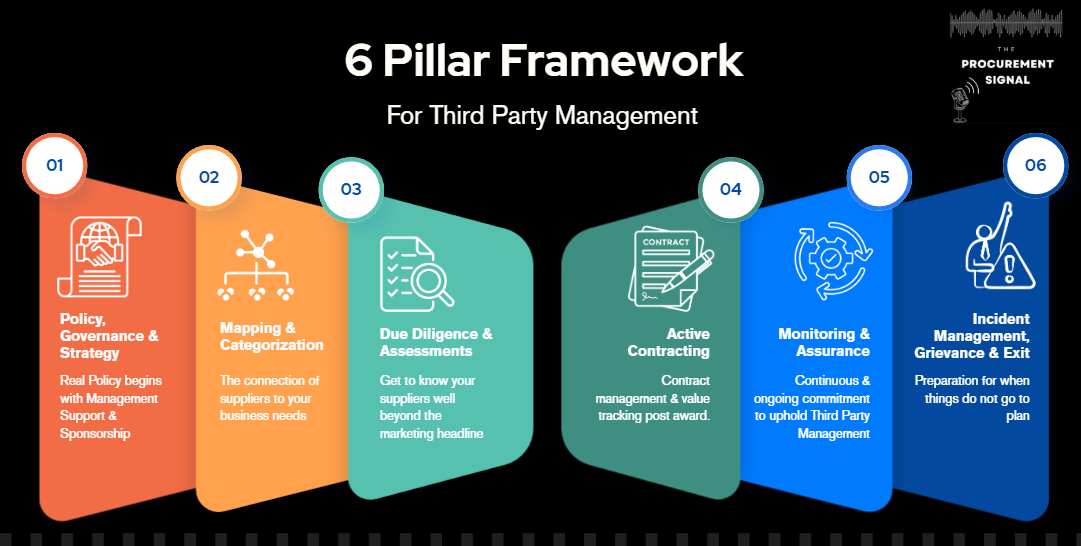
Procurement is no longer just about negotiating contracts and cutting costs—it is your organization's frontline defense against enterprise, cyber, and ESG risk. Whether you are navigating financial resilience (APRA CPS 230/234), supply chain human rights (CSDDD / Modern Slavery), or sustainability targets (CSRD/ISO 20400), regulators all expect the exact same operational machinery.
This Universal Procurement Third-Party Framework consolidates these complex global standards into six clear, actionable pillars to keep your business compliant and resilient:
Policy, Governance & Strategy — Management sets the appetite, SMEs document it and the business follows it. However, most policies do not follow this sequence, so many policies turn into weightless statements.
Mapping & Categorization — Look beyond Tier 1 vendors to expose deep sub-tier (fourth party) concentration risks. Understand how every Third Party addresses your business need.
Due Diligence & Assessments — Replace generic self-declarations with audit-ready, verifiable evidence. Get to know your suppliers beyond the marketing headline.
Active Contracting — Don’t just sign the agreement but track its performance & compliance well into the lifecycle.
Monitoring & Assurance — Shift from "one-and-done" onboarding to live threat monitoring. Build confidence in your Third-Party relationships through assurance.
Incident Management, Grievance & Exit — Protect operational continuity with tight incident response windows, give the power to report & carefully plan exits to minimize negative consequences.